
Page 1
START WITH A G U I D E F O R B U S I N E S S FEDERAL TRADE COMMISSION L E S S O N S L E A R N E D F R O M F T C C A S E S
A June 2015 FTC guide presenting ten practical data security lessons drawn from its enforcement cases. It covers data minimization, access controls, authentication, encryption, network segmentation and monitoring, remote access, secure product development, service provider oversight, vulnerability management, and physical security. The guide explains alleged security lapses and measures businesses could take to reduce risks, noting that the cited settlements are not court findings.
The first 5 pages, shown as text so search engines and readers can find this document.
START WITH A G U I D E F O R B U S I N E S S FEDERAL TRADE COMMISSION L E S S O N S L E A R N E D F R O M F T C C A S E S
1. Start with security. 2. Control access to data sensibly. 3. Require secure passwords and authentication. 4. Store sensitive personal information securely and protect it during transmission. 5. Segment your network and monitor who’s trying to get in and out. 6. Secure remote access to your network. 7. Apply sound security practices when developing new products. 8. Make sure your service providers implement reasonable security measures. 9. Put procedures in place to keep your security current and address vulnerabilities that may arise. 10. Secure paper, physical media, and devices. START WITH
1 When managing your network, developing an app, or even organizing paper files, sound security is no accident. Companies that consider security from the start assess their options and make reasonable choices based on the nature of their business and the sensitivity of the information involved. Threats to data may transform over time, but the fundamentals of sound security remain constant. As the Federal Trade Commission outlined in Protecting Personal Information: A Guide for Business, you should know what personal information you have in your files and on your computers, and keep only what you need for your business. You should protect the information that you keep, and properly dispose of what you no longer need. And, of course, you should create a plan to respond to security incidents. In addition to Protecting Personal Information, the FTC has resources to help you think through how those principles apply to your business. There’s an online tutorial to help train your employees; publications to address particular data security challenges; and news releases, blog posts, and guidance to help you identify – and possibly prevent – pitfalls. There’s another source of information about keeping sensitive data secure: the lessons learned from the more than 50 law enforcement actions the FTC has announced so far. These are settlements – no findings have been made by a court – and the specifics of the orders apply just to those companies, of course. But learning about alleged lapses that led to law enforcement can help your company improve its practices. And most of these alleged practices involve basic, fundamental security missteps. Distilling the facts of those cases down to their essence, here are ten lessons to learn that touch on vulnerabilities that could affect your company, along with practical guidance on how to reduce the risks they pose.
2 Start with security. From personal data on employment applications to network files with customers’ credit card numbers, sensitive information pervades every part of many companies. Business executives often ask how to manage confidential information. Experts agree on the key first step: Start with security. Factor it into the decisionmaking in every department of your business – personnel, sales, accounting, information technology, etc. Collecting and maintaining information “just because” is no longer a sound business strategy. Savvy companies think through the implication of their data decisions. By making conscious choices about the kind of information you collect, how long you keep it, and who can access it, you can reduce the risk of a data compromise down the road. Of course, all of those decisions will depend on the nature of your business. Lessons from FTC cases illustrate the benefits of building security in from the start by going lean and mean in your data collection, retention, and use policies. Don’t collect personal information you don’t need. Here’s a foundational principle to inform your initial decision-making: No one can steal what you don’t have. When does your company ask people for sensitive information? Perhaps when they’re registering online or setting up a new account. When was the last time you looked at that process to make sure you really need everything you ask for? That’s the lesson to learn from a number of FTC cases. For example, the FTC’s complaint against RockYou charged that the company collected lots of information during the site registration process, including the user’s email address and email password. By collecting email passwords – not something the business needed – and then storing them in clear text, the FTC said the company created an unnecessary risk to people’s email accounts. The business could have avoided that risk simply by not collecting sensitive information in the first place. Hold on to information only as long as you have a legitimate business need. Sometimes it’s necessary to collect personal data as part of a transaction. But once the deal is done, it may be unwise to keep it. In the FTC’s BJ’s Wholesale Club case, the company collected customers’ credit and debit card information to process transactions in its retail stores. But according to the complaint, it continued to store that data for up to 30 days – long after the sale was complete. Not only did that violate bank rules, but by holding on to the information without a legitimate business need, the FTC said BJ’s Wholesale Club created an unreasonable risk. By exploiting other weaknesses in the company’s security practices, hackers stole the account data and used it to make counterfeit credit and debit cards. The business could have limited its risk by securely disposing of the financial information once it no longer had a legitimate need for it. 1
3 Don’t use personal information when it’s not necessary. You wouldn’t juggle with a Ming vase. Nor should businesses use personal information in contexts that create unnecessary risks. In the Accretive case, the FTC alleged that the company used real people’s personal information in employee training sessions, and then failed to remove the information from employees’ computers after the sessions were over. Similarly, in foru International, the FTC charged that the company gave access to sensitive consumer data to service providers who were developing applications for the company. In both cases, the risk could have been avoided by using fictitious information for training or development purposes. Control access to data sensibly. Once you’ve decided you have a legitimate business need to hold on to sensitive data, take reasonable steps to keep it secure. You’ll want to keep it from the prying eyes of outsiders, of course, but what about your own employees? Not everyone on your staff needs unrestricted access to your network and the information stored on it. Put controls in place to make sure employees have access only on a “need to know” basis. For your network, consider steps such as separate user accounts to limit access to the places where personal data is stored or to control who can use particular databases. For paper files, external drives, disks, etc., an access control could be as simple as a locked file cabinet. When thinking about how to control access to sensitive information in your possession, consider these lessons from FTC cases. Restrict access to sensitive data. If employees don’t have to use personal information as part of their job, there’s no need for them to have access to it. For example, in Goal Financial, the FTC alleged that the company failed to restrict employee access to personal information stored in paper files and on its network. As a result, a group of employees transferred more than 7,000 consumer files containing sensitive information to third parties without authorization. The company could have prevented that misstep by implementing proper controls and ensuring that only authorized employees with a business need had access to people’s personal information. 2
Doxxly editorial guide
This guide helps you understand the scope of Start with Security: A Guide for Business - Lessons Learned from FTC Cases before or alongside reading the original document. It is based on the catalogue record, credited creator, source, classification and topics shown on this page. It does not replace the original work and does not invent claims about passages that Doxxly cannot verify.
Start with Security: A Guide for Business - Lessons Learned from FTC Cases is a 20-page documentcredited to Rhea H. Yarrow. A June 2015 FTC guide presenting ten practical data security lessons drawn from its enforcement cases. It covers data minimization, access controls, authentication, encryption, network segmentation and monitoring, remote access, secure product development, service provider oversight, vulnerability management, and physical security. The guide explains alleged security lapses and measures businesses could take to reduce risks, noting that the cited settlements are not court findings. It appears in the Technology & Security collection, which groups it with other material that readers may use for comparison and further study.
The item can be approached in several ways. A reader looking for a quick orientation can begin with the free five-page preview, inspect the page structure and use the metadata to judge relevance. Someone undertaking deeper research can work through the complete file, search its indexed text, record useful page references and compare its treatment of Data security, Business guidance, Federal Trade Commission, Personal information protection, Access control, Secure software development, Vendor security, Vulnerability management, Physical security with the related resources linked below.
Rather than reducing the work to a single claim, this page treats it as a source that should be read in context. The title, creator, publication source, licence and format all help explain what kind of evidence it may offer. Readers should distinguish the original author's statements from Doxxly's catalogue description, and should cite the original edition when using the material in academic, professional or published work.
The catalogue connects this document with Data security, Business guidance, Federal Trade Commission, Personal information protection, Access control, Secure software development, Vendor security, Vulnerability management, Physical security. These terms offer practical entry points rather than a substitute for close reading. Start by identifying the definitions, examples, arguments, tables or visual explanations attached to each topic. Then note where the creator draws connections, makes distinctions or moves from background material to a conclusion, recommendation, calculation or narrative development.
A useful reading method is to separate description from interpretation. First record what the item actually presents: names, headings, figures, formulas, quotations or stated propositions. Next consider why those details matter within the whole work. Finally compare them with another source from the same subject area. This process helps turn a long digital file into evidence that can be evaluated rather than merely skimmed.
The following is an editorial content guide based on the verified catalogue topics. It is not represented as the original author's formal table of contents. Use it to organise notes while moving through the 20 pages in the player.
Use this section of the reading guide to identify how Data security appears in Start with Security: A Guide for Business - Lessons Learned from FTC Cases, note important terms, and connect the subject to the wider purpose of the work.
Use this section of the reading guide to identify how Business guidance appears in Start with Security: A Guide for Business - Lessons Learned from FTC Cases, note important terms, and connect the subject to the wider purpose of the work.
Use this section of the reading guide to identify how Federal Trade Commission appears in Start with Security: A Guide for Business - Lessons Learned from FTC Cases, note important terms, and connect the subject to the wider purpose of the work.
Use this section of the reading guide to identify how Personal information protection appears in Start with Security: A Guide for Business - Lessons Learned from FTC Cases, note important terms, and connect the subject to the wider purpose of the work.
Use this section of the reading guide to identify how Access control appears in Start with Security: A Guide for Business - Lessons Learned from FTC Cases, note important terms, and connect the subject to the wider purpose of the work.
Use this section of the reading guide to identify how Secure software development appears in Start with Security: A Guide for Business - Lessons Learned from FTC Cases, note important terms, and connect the subject to the wider purpose of the work.
Use this section of the reading guide to identify how Vendor security appears in Start with Security: A Guide for Business - Lessons Learned from FTC Cases, note important terms, and connect the subject to the wider purpose of the work.
Use this section of the reading guide to identify how Vulnerability management appears in Start with Security: A Guide for Business - Lessons Learned from FTC Cases, note important terms, and connect the subject to the wider purpose of the work.
When a heading in the original differs from this guide, follow the original heading in your citation. Page numbers can also vary between editions. Doxxly's direct page field is useful for navigation, but formal references should include the title, creator, source and edition details available in the file itself.
Doxxly credits Rhea H. Yarrow as the author or creator of Start with Security: A Guide for Business - Lessons Learned from FTC Cases. This page does not add an unverified biography, job title or institutional affiliation. The attribution is preserved so readers can distinguish the creator from the hosting library and follow the original record when an external author link is available.
Author context matters because a work reflects a particular purpose, audience and point of view. Before relying on the material, consider what the creator set out to explain, when the source was produced and whether later research or revised guidance should also be consulted. For literature and philosophy, compare translations and editions; for technical material, check whether a newer version has superseded the one shown here.
The recorded source for this item is ftc.gov. Doxxly provides access and discovery tools but does not claim to be the original publisher unless explicitly stated. Source links, creator attribution and the recorded Publicly available file collected for editorial review licence are displayed to help readers assess provenance and permitted use.
Provenance is especially important for reports, standards, presentations and working spreadsheets. Check the original source for amendments, supporting files and current policy. A trustworthy research workflow keeps the source URL with any notes or downloaded copy, verifies important figures against the original, and avoids treating an archived document as automatically current.
Visit ftc.govBegin with the title and opening pages, then use the guide above to decide whether to read sequentially or move to a particular topic. The Doxxly player provides previous and next navigation, a direct page field, zoom steps, fit-to-width and fit-to-page modes, rotation and fullscreen. These controls are useful when a page contains small type, a wide table, an image, a scanned layout or a dense sequence of notes.
The first five pages are open to every visitor. A plan unlocks the complete item and full-document search. Search is best used for distinctive names, technical terms or short phrases; broad words can produce too many possible contexts. When you find a useful passage, read the surrounding pages so that a sentence, chart or formula is not separated from its explanation.
If downloading is enabled, members can obtain the original PDF file. Keep the original format when formulas, slide sequencing, pagination or layout carries meaning. Respect the Publicly available file collected for editorial review terms displayed on this page, and use the rights-report link if you believe the attribution or availability needs review.
As you read Start with Security: A Guide for Business - Lessons Learned from FTC Cases, ask which audience the creator addresses, what problem or idea organises the work, what evidence is presented, and which assumptions remain unstated. Note whether important terms are defined consistently and whether examples represent a broader pattern or a narrow case. For quantitative material, record units, time periods, formulas and data sources. For interpretive material, separate the creator's language from your own summary.
A second set of questions concerns relevance today. Which parts remain durable, which depend on their historical or institutional setting, and what would need confirmation from a newer source? Following the tags and the Technology & Security collection can reveal useful comparisons. Agreement between sources can strengthen confidence, while disagreement can point to changing definitions, methods, evidence or priorities.
Finally, decide what you need from the item: background knowledge, a quotation, a worked example, a model, a visual explanation or a starting bibliography. That purpose should guide the depth of reading and the notes you keep. Doxxly helps locate and navigate the source; careful interpretation remains the reader's responsibility.
Practical answers about reading, downloading and understanding this document on Doxxly.
National Institute of Standards and Technology
National Institute of Standards and Technology
National Institute of Standards and Technology
National Institute of Standards and Technology
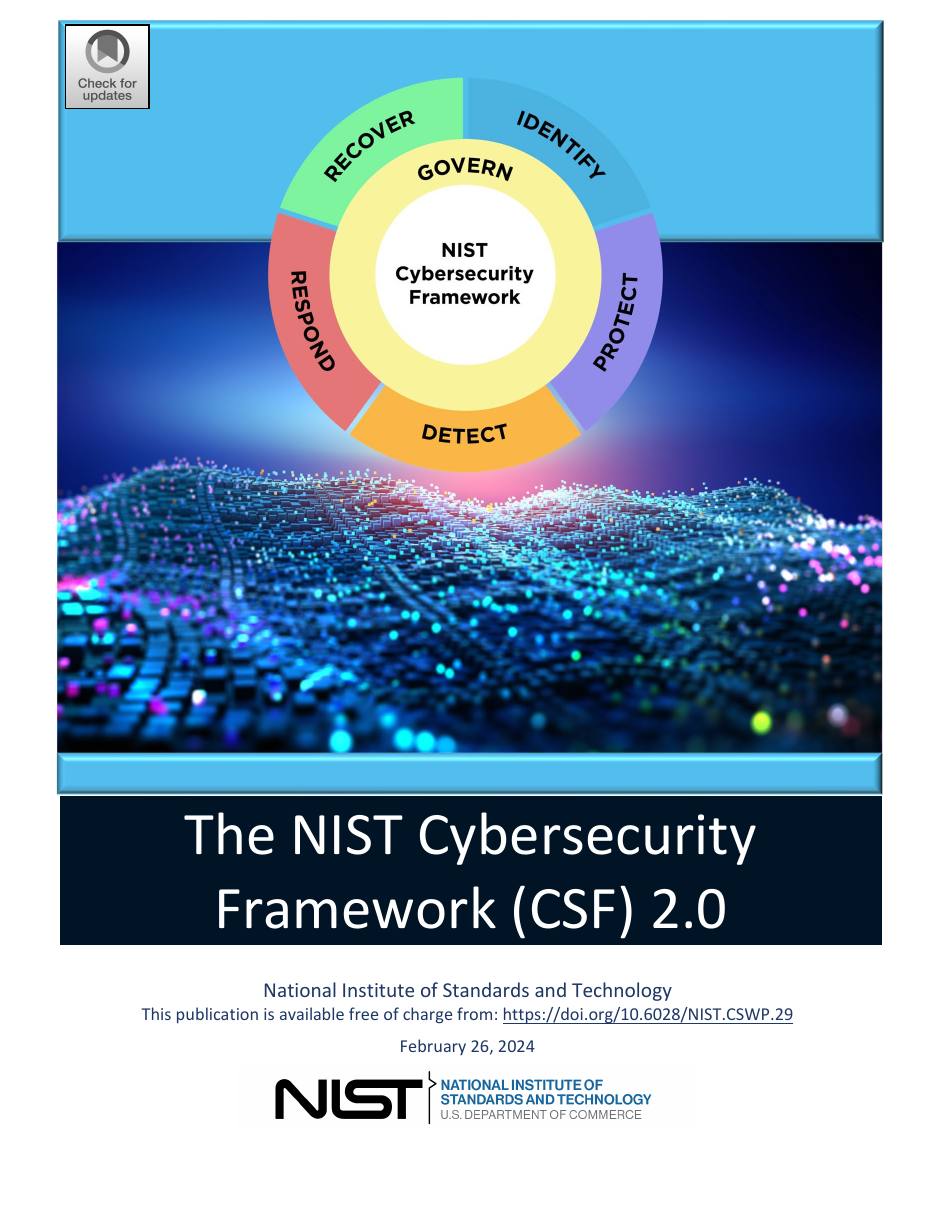
National Institute of Standards and Technology
National Institute of Standards and Technology